A look into Corporate fraud in Australia, Stranglehold of Monopolies, Telecom's Oppression, Biased Law System, Corporate influence in politics, Industrial Relations disadvantaging workers, Outsourcing Australian Jobs, Offshore Banking, Petrochemical company domination, Invisibly Visible.
It's not what you see, it's what goes on behind the scenes. Australia, the warrantless colony.
Note: Site has more info in desktop mode or 'web version' as seen at bottom of page, when on smartphone.
COMMONWEALTH OF AUSTRALIA (ABN: 122 104 616)
Australia's Prime Minister (CEO) Tony Abbott : "Australia is Open for Business"
It seems that the Victorian Government is enticing / forcing / mandating persons to download an app for the purposes of contract tracing, in direct conflict with federal law.
While the federal law Section 94H of the Privacy Act 1988 or the Privacy Amendment (Public Health Contact Information) Act 2020 mentions a specific app, the purpose of that app/program is for contact tracing.
Since this information is on the government's website, and not in any 'Act' this requirement or 'suggestion' can be ignored.
There is a oppressive push for governments and corporations
to obtain more personal data under the auspice of being in the interest of
public health but this could not be further from the truth.
Before you were told that you must use a government sponsored
white elephant called the COVIDSafe app when you leave your home or enter a business/public
premises.
But there is one huge problem with that.
NO person can force you the user/customer/consumer/product to use
this program.
It is against the law.
To be more specific, against Section 94H of the Commonwealth
law called the Privacy Act 1988.
This also appears in another law, that being the Privacy Amendment
(Public Health Contact Information) Act 2020, under the same section as the
above Act.
Samsung, Xiaomi and Oppo users of Google's versions of Android prior to version 12 would have their screenshots put up on the internet.
This is not a 'bug' or an 'error' but rather a deliberate(?) attempt a obtaining information of what people are interested in, WITHOUT their knowledge or consent.
Realistically, the companies involved should be sued, en masse.
We do not recommend the use of OEM (Original Equipment Manufacturer), versions of Android, which contain malicious closed source code inserted by Google.
Instead we recommend the use of Android in its purest form called AOSP (Android Open Source Project), which is open source and is scrutinised by security researchers where it does not contain any tracking or malicious code.
Some of the groups that maintain and make AOSP available are:
The Victorian government has been caught out stating false
information in relation to an exposure site.
Social media users were greeted in the early afternoon of Tuesday the 18th of
May 2021, with a message from the Victorian Department of Health that there is
a new exposure site, in the CBD of Melbourne.
They were also given instructions on what to do.
There is one HUGE problem with this.
The fact is that there is no new exposure at any site
whatsoever.
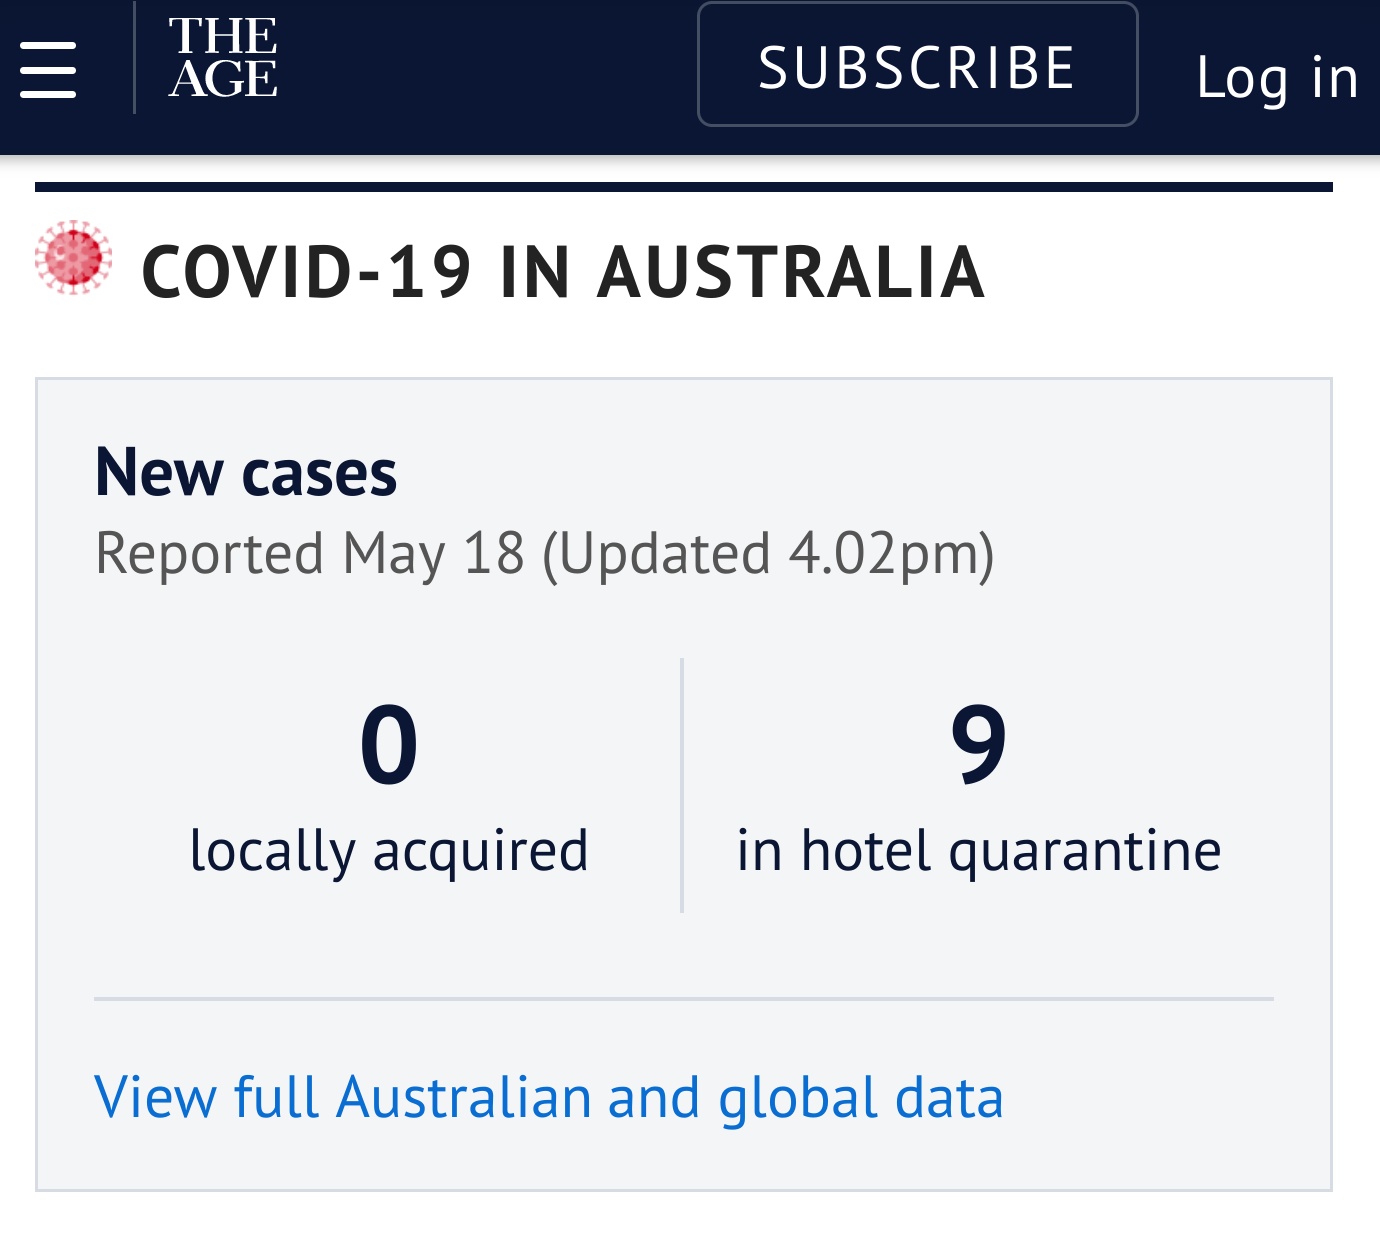
In fact there have been no alleged cases since the 7th
of May 2021, or 11 days prior according to the site that reported that there is a new case today.
They blatantly lied.
The post has been reported to the administrators of the
social media site, but we have very little faith that any posts from the
Victorian Department of Health will be stopped, as ‘we’ that taxpayers are
paying the social media site for this false information, where the site profits
from every post from the VDoH puts up.
MANY a lesser person’s posts have been banned for much less of
a so called excuse.
Apple and Google are a danger to your privacy where also the
goal is to stamp out ‘anonymity’ on the internet.
The two companies are born into the five eyes, top tier global
surveillance régime, where ultimately your data ends up in various so called ‘government’
departments or whoever else they subcontract out to without your knowledge or
even consent.
Technical experts have exposed the fact the Apple’s new Bluetooth
product the AirTag can be hacked and used for nefarious purposes, but it’s not
the privacy culprit it’s made out to be.
You are of zero use to corporations (e.g. Apple) if you only
purchase their product once, or even once in 10 years, using the principle ‘if
it’s ain’t broke, don’t fix it’, so they have an enormous budget set aside for
marketing, to bedazzle consumers to purchase this ½ year model update where the
in colour is purple and they must buy it in order to remain cool/tech savvy/modern.
Apple, the masters of marketing or rather deception, work on
the human emotion of desire to sell their underwhelming and lacklustre featured phones, where they have established a huge following which in the industry is
called ‘fan boys’.
Just because Apple’s advertisements talk about privacy does
not really mean that they’re truly private.
What’s worse is the logic of Apple’s fan boys where a mindset
is that gay users trust what Tim Cook says because he's gay.
One’s sexual orientation has nothing to do with the business
or policies of the corporation.
Mainstream so called tech journalists are nothing more than
flogs promoting the warez with zero in-depth analysis of the products
concerned.
Apple’s AirTag is not the culprit, in the war against you privacy,
where it’s only the half culprit, the enabler, where the iPhone/iPad is the
other half.
Why is there such an oppressive push to purchase the new
iPhone?
Newer hardware (and software) enables corporations and
governments to acquire more data, more efficiently and best of all, at your
expense.
With the new iPhone comes new software which is called
malware within the industry as it’s embedded into the phone, tracing your every
move, always turned on, where you as the ‘owner’ of the phone have zero control over that part of the phone's operation.
One of the key ingredients in this user sponsored global spy
network is the humble invention called Bluetooth.
Gone are the days where this protocol could only communicate
10 meters or 100m, where now it can go as far as 240m (line of sight) and 40m
inside.
The malware that Apple and Google have ‘baked’ into your
phone carries out the constantly on functions of Wi-Fi scanning and Bluetooth scanning
in order to trace your every move.
Your iPhone, is used constantly to log your
position, where the AirTag is the trigger then your iPhone is used to pass data on,
a total disaster for your privacy, irrespective of the claims that Apple may make with regard to encryption.
For Apple users there is no privacy solution, where if privacy
is truly your concern (which it should be) then it would be followed by the action of ‘throwing away’
your Apple device.
For Android users, there is a solution that being to ‘de-Google’
your phone, which means to install the bare bones version of Android called
AOSP, which can only be done on certain phones.
IF Apple were to claim that there is truly no concern with regards to your privacy, then show us the source code, as 'nothing to hide nothing to fear' saying applies, where the concern of 'Intellectual Property' is irrelevant.
With the use of Apple products you're enabling this 'Skynet' to exist.
See article, Flashback: a brief history of Bluetooth at:
A new release published by Italy’s Antitrust Authority calls out
Google for its “abuse of dominant position” and fined Google for €100
million on the grounds that Google excluded Enel X’s app JuicePass, an
app that helps drivers find and reserve spots at charging stations.
The case against Google is that the Authority’s investigation found
Google excluded the JuicePass app from the Android Auto Platform for
more than two years. “According to the Authority’s findings, Google did
not allow Enel X Italia to develop a version of its JuicePass app
compatible with Android Auto.
Italy’s Antitrust Authority issued a cease-and-desist order to Google
with details on how it should respond in order to “stop the abuse and
avoid the negative effects of the exclusion of Enel X Italia’s app from
Android Auto.” Google is ordered to allow Enel X Italia on the platform,
as well offer tools to other app developers who want to make apps for
Android Auto.
In Google’s defense, the reason for why JuicePass hasn’t been
approved for Android Auto is not mentioned. A spokesperson for Google
Italy told Reuters that Google “respectfully disagrees” with the
Authority’s decision. Google prioritizes safety on Android Auto and it
has strict guidelines on which apps it supports, according to the Google
spokesperson.
Meanwhile, Enel X is aware of the decision and hopes that the outcome
will grant “a level playing field with Google Apps” for JuicePass and
all recharging app developers.
As time goes by, two of the world’s largest data collection
corporations, Apple and Google obtain more and more data on you, where later
this data is used against you.
One of the key ingredients with regards to data collection
is to obtain your person’s identity.
Under the guise of security (an now allegedly heath), Google
needs to obtain your phone number which is linked to your identity in order to
collect more data under that identity.
How is Google going to do this?
By some things called:
1). Two step verification (2FV),
2). Two Factor Authentication (2FA)
To read more on this topic, see the following articles:
As a result
of the recent ‘failure of government’ with regards to an alleged ‘case’ in
Victoria, the retaliation by government could be to suggest the solution that being the mandatory use of QR code scanning by consumers prior to engaging in
commerce with a business.
There’s a
few problems with that.
Firstly
making such an action mandatory is illegal, see Section 94H of the Privacy Act 1988, even though this refers to an app, where the purpose of the QR code scan is the same as the app.
The person
that allegedly tested positive was tested by an inaccurate procedure used by
the government, see references below.
The action of
QR code scanning had nothing to do with the failure of government in relation
to the so called ‘case’.
The ASD
(Australian Signals Directorate) warns that scanning QR code can lead to your
data being used for criminal purposes.
Prior to
scanning ANY QR code, here are just some questions that need to be answered:
- If one is
required at law to perform an action, where one does not have the required
equipment, will the government provide that person with the required equipment?
- Where does
your data go once you’ve scanned?
- Can you
obtain the ‘source code’ from the website in relation to where your data is distributed/stored?
- Did the
website business obtain government protocols on how to handle the data?
- What penalties are in force if there is 'mismanagement' of data?
- Can you
obtain a PDS (Product Disclosure Statement) PRIOR to scanning the code?
(as you are
entering into a business transaction with an EXTERNAL entity, where you are not
given the full ‘Terms & Conditions’ in relation to this new transaction
i.e. scanning the QR code)
In relation to the government's claim that the person is a COVID-19 'case', what number of cycles were used in his test?
The government may say to you that an action is not 'mandatory' but if you do not comply, you will receive an exorbitant /disproportionate fine.
The people in government are human rights abusers, remembering that the Victorian premier Daniel Andrews stated that it's not about human rights (with regards to new law being put in place, where in fact the law MUST be in line with human rights, and signed off that it is).
The people in government commit many illegal and criminal actions, where it is up to you to catch them out make it public knowledge, and put the matter before the courts, in order to 'keep the bastards honest'.
According to the government, the state of Victoria has
recorded an alleged COVID-19 ‘case’, that being a person who allegedly has the
SARS-CoV-2 virus.
Remembering that the state recorded a zero for quite
some time, meaning that no one in the community had the virus, where the people
were told once before that we ‘eliminated’ the virus.
Since the cat is out of the bag with relation to this person
being from overseas, the government failed to take the appropriate measure to
safeguard the general population, that's assuming the person actually has the virus.
The more important aspect is that the testing done is factually
inaccurate.
If you have been tested for ‘covid’ it is your right or
rather your duty to obtain the result, and not an SMS or verbal message whether
you are positive or negative.
This is how your covid test result should look like:
('Customer' details have been blocked out)
After all, you’ve heard the saying that is used on you by those in position of power?
“Nothing to hide, nothing to fear”, right?
ASK how many cycles was the test carried out at.
DEMAND that to be in the report.
Since the ‘case’ result is a farce, why do the people have
to be punished by a government failure?
Why must there be a mandate for people to wear a mask, if
this is a useless exercise?
Why must people's movements be restricted if that has nothing
to do with us?