A look into Corporate fraud in Australia, Stranglehold of Monopolies, Telecom's Oppression, Biased Law System, Corporate influence in politics, Industrial Relations disadvantaging workers, Outsourcing Australian Jobs, Offshore Banking, Petrochemical company domination, Invisibly Visible.
It's not what you see, it's what goes on behind the scenes. Australia, the warrantless colony.
Note: Site has more info in desktop mode or 'web version' as seen at bottom of page, when on smartphone.
COMMONWEALTH OF AUSTRALIA (ABN: 122 104 616)
Australia's Prime Minister (CEO) Tony Abbott : "Australia is Open for Business"
The Victorian government has been caught out stating false
information in relation to an exposure site.
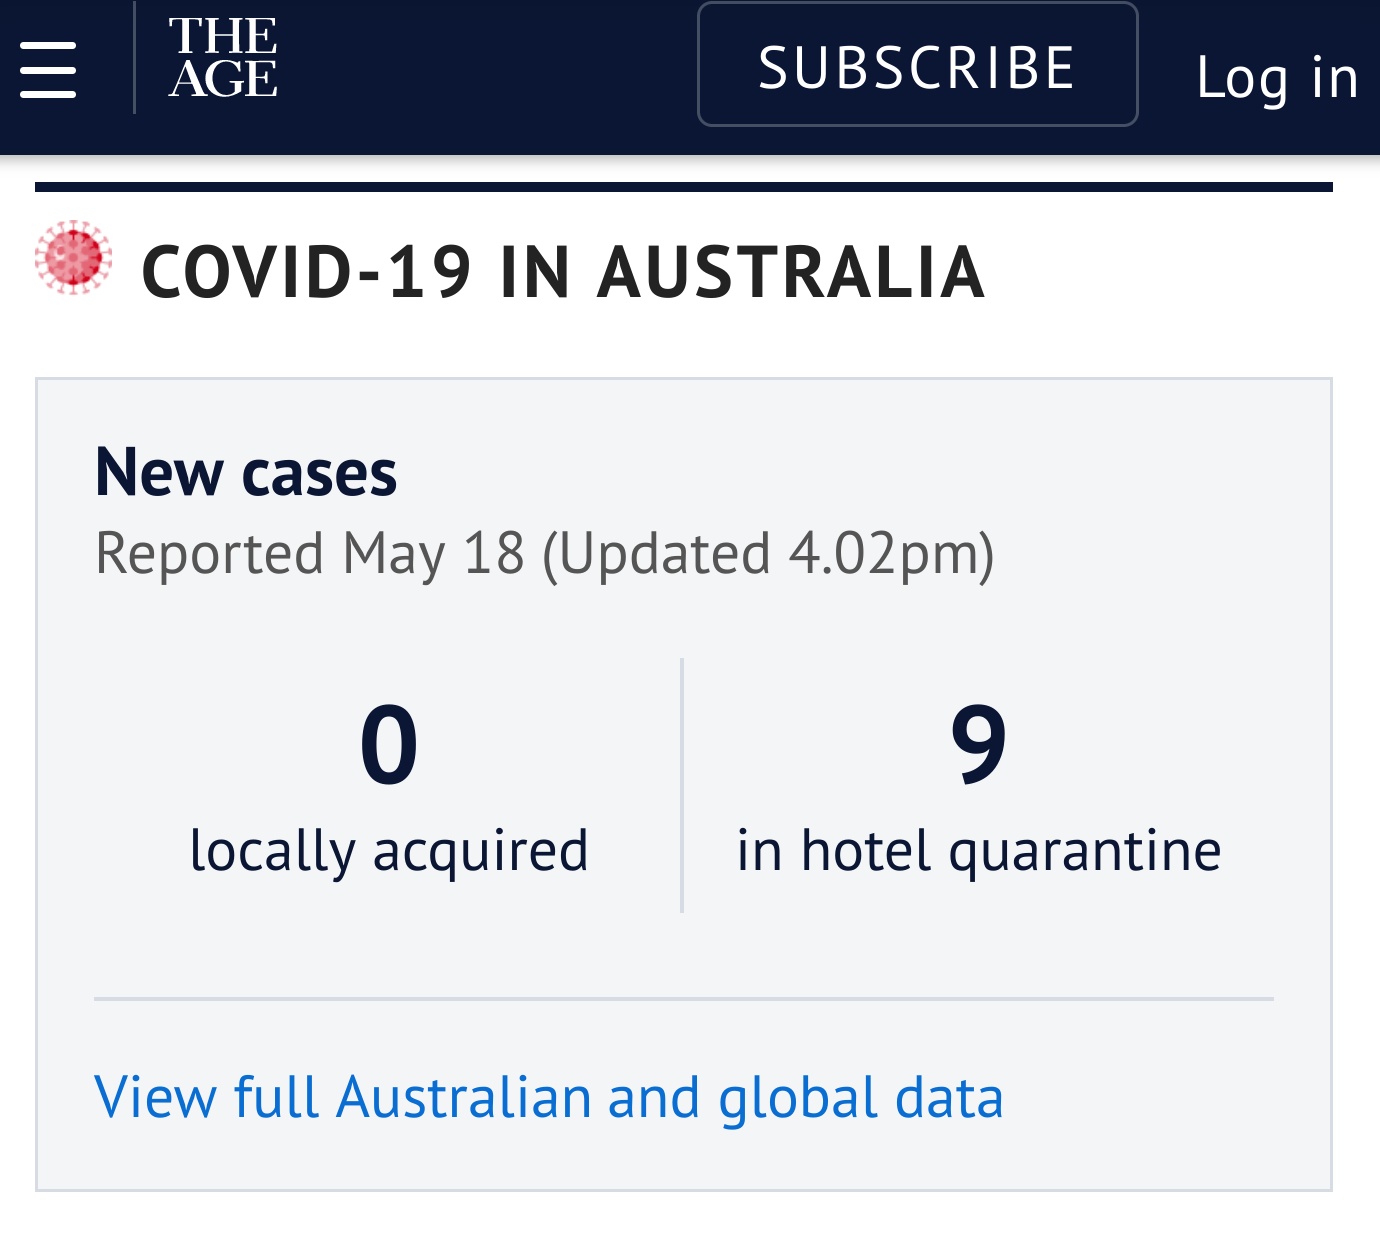
Social media users were greeted in the early afternoon of Tuesday the 18th of
May 2021, with a message from the Victorian Department of Health that there is
a new exposure site, in the CBD of Melbourne.
They were also given instructions on what to do.
There is one HUGE problem with this.
The fact is that there is no new exposure at any site
whatsoever.
In fact there have been no alleged cases since the 7th
of May 2021, or 11 days prior according to the site that reported that there is a new case today.
They blatantly lied.
The post has been reported to the administrators of the
social media site, but we have very little faith that any posts from the
Victorian Department of Health will be stopped, as ‘we’ that taxpayers are
paying the social media site for this false information, where the site profits
from every post from the VDoH puts up.
MANY a lesser person’s posts have been banned for much less of
a so called excuse.
Apple and Google are a danger to your privacy where also the
goal is to stamp out ‘anonymity’ on the internet.
The two companies are born into the five eyes, top tier global
surveillance régime, where ultimately your data ends up in various so called ‘government’
departments or whoever else they subcontract out to without your knowledge or
even consent.
Technical experts have exposed the fact the Apple’s new Bluetooth
product the AirTag can be hacked and used for nefarious purposes, but it’s not
the privacy culprit it’s made out to be.
You are of zero use to corporations (e.g. Apple) if you only
purchase their product once, or even once in 10 years, using the principle ‘if
it’s ain’t broke, don’t fix it’, so they have an enormous budget set aside for
marketing, to bedazzle consumers to purchase this ½ year model update where the
in colour is purple and they must buy it in order to remain cool/tech savvy/modern.
Apple, the masters of marketing or rather deception, work on
the human emotion of desire to sell their underwhelming and lacklustre featured phones, where they have established a huge following which in the industry is
called ‘fan boys’.
Just because Apple’s advertisements talk about privacy does
not really mean that they’re truly private.
What’s worse is the logic of Apple’s fan boys where a mindset
is that gay users trust what Tim Cook says because he's gay.
One’s sexual orientation has nothing to do with the business
or policies of the corporation.
Mainstream so called tech journalists are nothing more than
flogs promoting the warez with zero in-depth analysis of the products
concerned.
Apple’s AirTag is not the culprit, in the war against you privacy,
where it’s only the half culprit, the enabler, where the iPhone/iPad is the
other half.
Why is there such an oppressive push to purchase the new
iPhone?
Newer hardware (and software) enables corporations and
governments to acquire more data, more efficiently and best of all, at your
expense.
With the new iPhone comes new software which is called
malware within the industry as it’s embedded into the phone, tracing your every
move, always turned on, where you as the ‘owner’ of the phone have zero control over that part of the phone's operation.
One of the key ingredients in this user sponsored global spy
network is the humble invention called Bluetooth.
Gone are the days where this protocol could only communicate
10 meters or 100m, where now it can go as far as 240m (line of sight) and 40m
inside.
The malware that Apple and Google have ‘baked’ into your
phone carries out the constantly on functions of Wi-Fi scanning and Bluetooth scanning
in order to trace your every move.
Your iPhone, is used constantly to log your
position, where the AirTag is the trigger then your iPhone is used to pass data on,
a total disaster for your privacy, irrespective of the claims that Apple may make with regard to encryption.
For Apple users there is no privacy solution, where if privacy
is truly your concern (which it should be) then it would be followed by the action of ‘throwing away’
your Apple device.
For Android users, there is a solution that being to ‘de-Google’
your phone, which means to install the bare bones version of Android called
AOSP, which can only be done on certain phones.
IF Apple were to claim that there is truly no concern with regards to your privacy, then show us the source code, as 'nothing to hide nothing to fear' saying applies, where the concern of 'Intellectual Property' is irrelevant.
With the use of Apple products you're enabling this 'Skynet' to exist.
See article, Flashback: a brief history of Bluetooth at:
A new release published by Italy’s Antitrust Authority calls out
Google for its “abuse of dominant position” and fined Google for €100
million on the grounds that Google excluded Enel X’s app JuicePass, an
app that helps drivers find and reserve spots at charging stations.
The case against Google is that the Authority’s investigation found
Google excluded the JuicePass app from the Android Auto Platform for
more than two years. “According to the Authority’s findings, Google did
not allow Enel X Italia to develop a version of its JuicePass app
compatible with Android Auto.
Italy’s Antitrust Authority issued a cease-and-desist order to Google
with details on how it should respond in order to “stop the abuse and
avoid the negative effects of the exclusion of Enel X Italia’s app from
Android Auto.” Google is ordered to allow Enel X Italia on the platform,
as well offer tools to other app developers who want to make apps for
Android Auto.
In Google’s defense, the reason for why JuicePass hasn’t been
approved for Android Auto is not mentioned. A spokesperson for Google
Italy told Reuters that Google “respectfully disagrees” with the
Authority’s decision. Google prioritizes safety on Android Auto and it
has strict guidelines on which apps it supports, according to the Google
spokesperson.
Meanwhile, Enel X is aware of the decision and hopes that the outcome
will grant “a level playing field with Google Apps” for JuicePass and
all recharging app developers.
As time goes by, two of the world’s largest data collection
corporations, Apple and Google obtain more and more data on you, where later
this data is used against you.
One of the key ingredients with regards to data collection
is to obtain your person’s identity.
Under the guise of security (an now allegedly heath), Google
needs to obtain your phone number which is linked to your identity in order to
collect more data under that identity.
How is Google going to do this?
By some things called:
1). Two step verification (2FV),
2). Two Factor Authentication (2FA)
To read more on this topic, see the following articles:
As a result
of the recent ‘failure of government’ with regards to an alleged ‘case’ in
Victoria, the retaliation by government could be to suggest the solution that being the mandatory use of QR code scanning by consumers prior to engaging in
commerce with a business.
There’s a
few problems with that.
Firstly
making such an action mandatory is illegal, see Section 94H of the Privacy Act 1988, even though this refers to an app, where the purpose of the QR code scan is the same as the app.
The person
that allegedly tested positive was tested by an inaccurate procedure used by
the government, see references below.
The action of
QR code scanning had nothing to do with the failure of government in relation
to the so called ‘case’.
The ASD
(Australian Signals Directorate) warns that scanning QR code can lead to your
data being used for criminal purposes.
Prior to
scanning ANY QR code, here are just some questions that need to be answered:
- If one is
required at law to perform an action, where one does not have the required
equipment, will the government provide that person with the required equipment?
- Where does
your data go once you’ve scanned?
- Can you
obtain the ‘source code’ from the website in relation to where your data is distributed/stored?
- Did the
website business obtain government protocols on how to handle the data?
- What penalties are in force if there is 'mismanagement' of data?
- Can you
obtain a PDS (Product Disclosure Statement) PRIOR to scanning the code?
(as you are
entering into a business transaction with an EXTERNAL entity, where you are not
given the full ‘Terms & Conditions’ in relation to this new transaction
i.e. scanning the QR code)
In relation to the government's claim that the person is a COVID-19 'case', what number of cycles were used in his test?
The government may say to you that an action is not 'mandatory' but if you do not comply, you will receive an exorbitant /disproportionate fine.
The people in government are human rights abusers, remembering that the Victorian premier Daniel Andrews stated that it's not about human rights (with regards to new law being put in place, where in fact the law MUST be in line with human rights, and signed off that it is).
The people in government commit many illegal and criminal actions, where it is up to you to catch them out make it public knowledge, and put the matter before the courts, in order to 'keep the bastards honest'.
According to the government, the state of Victoria has
recorded an alleged COVID-19 ‘case’, that being a person who allegedly has the
SARS-CoV-2 virus.
Remembering that the state recorded a zero for quite
some time, meaning that no one in the community had the virus, where the people
were told once before that we ‘eliminated’ the virus.
Since the cat is out of the bag with relation to this person
being from overseas, the government failed to take the appropriate measure to
safeguard the general population, that's assuming the person actually has the virus.
The more important aspect is that the testing done is factually
inaccurate.
If you have been tested for ‘covid’ it is your right or
rather your duty to obtain the result, and not an SMS or verbal message whether
you are positive or negative.
This is how your covid test result should look like:
('Customer' details have been blocked out)
After all, you’ve heard the saying that is used on you by those in position of power?
“Nothing to hide, nothing to fear”, right?
ASK how many cycles was the test carried out at.
DEMAND that to be in the report.
Since the ‘case’ result is a farce, why do the people have
to be punished by a government failure?
Why must there be a mandate for people to wear a mask, if
this is a useless exercise?
Why must people's movements be restricted if that has nothing
to do with us?
According to its motherland, the colony we call
Australia is a legal ‘basket case’.
From instances like the ‘Queen of Australia’, the
Australia Act 1986 (yeah, which one), Constitution Act 1975 (Vic), Citizenship
Act 1948, ‘Ch. III courts’ and other occurrences in Australia’s timeline,
they're all done beyond the powers granted to the colony.
Contrary to popular belief and ‘false advertising’
by those in government, there is no separation of powers.
Separation of powers is supposed to exist within
the tree tiers of government, that being;
1). The Executive, Governors, Governor General, the
Queen,
2). Parliament, MPs bureaucrats,
3). The judicature, i.e. the people involved in the
administration of justice, including the police.
The separation of powers do not exist when people
from the above 3 tiers belong to the ‘brotherhood’, whether it be Freemasons,
Fabians or even the cult called Hillsong Church.
Whatever oath of office is taken it’s subverted by
the brotherhood’s oath, which is technically illegal, but as we know ‘everything
is legal, until you get caught’, well that saying applies to some.
Headlines were made when a Melbourne lawyer (i.e.
an officer of the court), lodged a class action lawsuit against the unlawful
lockdown of residents in housing commission accommodation, i.e. the
‘vulnerable’.
The moment it was lodged within the courts, her
ability to earn a living was taken from her by the VLSB (Victorian Legal
Services Board), where the legal enforceability is in question.
As usual this topic gained traction on social
media, by people who are referred to as Facebook lawyers, meaning a derogatory
term for people who have an incorrect opinion on law, irrespective of their
legal qualifications.
So, a person, let’s call him Greyham drew attention
to this lawyer’s case being in the Family Court that being “Kocak & Fahri
[2020] FamCA 652 (10 August 2020)”, where he stated that the lawyer “started to grift
to vulnerable potential clients”.
To make it even more absurd, good ol’ Grey’s
mentality is that the Austlii document is the court’s (i.e. the FCA's)
document, which it is not.
In any event we pity anyone trying to obtain some
legal advice from good ol’ ‘Greyham’.
So back to the brotherhood, they struck with a
premeditated vengeance against the Melbourne based lawyer from AdvocateMe, in
order to teach others not to go against the system.
Some other mildly retarded people on social media
will say that the lawyers in the Lawyer X, Informer 3838 matter exposed
corruption and nothing happened to them.
Sure, but what also Ms. Serene Teffaha exposed was
that with regards to that matter, was the support of paedophiles by the Family
Court.
With reference to the matter that was in the
spotlight on social media by ol’ Grey, ‘judge’ Nora Hartnett facilitated
children to be in the hands of an [accused] paedophile.
The matter also navigates through international
borders, which is an embarrassment to the Australian Government.
Researcher finds that the Apple AirTag can be hacked and reprogrammed to cause mischief
A German researcher by the name of stacksmashing disseminated a tweet
about his success hacking the Apple AirTag item tracker. He
reversed-engineered the microcontroller on the device (although he
bricked two AppleTag units while attempting to do this) and re-flashed
the microcontroller allowing him to make some changes to the AirTag's
functionality. The change made had to do with the URL that appears on a
notification when an AirTag in Lost Mode is tapped by an NFC-enabled
smartphone (iOS or Android).
When an AirTag is placed in Lost Mode, it sends out signals that can be picked up by the close to 1 billion active Apple
devices world wide. When an AirTag is discovered by this "Find My"
network," placing the AirTag close to an iPhone or an NFC-enabled
Android device will open a notification redirecting the person finding
the lost tag to a website (found.apple.com). Hopefully the owner of the
missing object remembered to add his contact information including a
phone number and a message.
Here's where the hack comes in. The German researcher changed the
URL on the notification. Instead of telling the person who discovered
the lost AirTag about the found.apple.com site, the notification
promoted the researcher's web site and included his URL.
This should be alarming to Apple
because the AirTag hack might allow someone to stalk a particular
AirTag user. Apple already sends out an alert when an AirTag that
doesn't belong is discovered "traveling" with a family. As for the
possibility that an AirTag can be hacked to create a security problem,
it looks like it has proven to be very possible and Apple will need to
respond.
Emails that have been published as part of the Epic Games v. Apple
trial have revealed that back in 2015, 128 million iOS users installed
2,500+ infected apps that were affected by the XcodeGhost malware. The
malware was placed inside apps that appeared to be legitimate and at the
time it was believed to be the largest hack against iPhone users based
on the number of people affected. Of the aforementioned 128 million
users impacted, 18 million were from the U.S.
128 million iOS users installed 2500+ malware infected apps in 2015 including popular titles like WeChat and Angry Birds 2
The malware was used to mine data from iOS users and Dale Bagwell,
Apple's manager of iTunes customer experience, said that there were 203
million downloads of the those 2500+ malware-laden apps. Another Apple
employee wrote in an email that "China represents 55% of customers and
66% of downloads. As you can see, a significant number (18 million
customers) are affected in the US."
The malware was supposed to be able to grab personal information
from victims including the name of the infected app, the name and type
of the device, network information and more. In its FAQ site, Apple
wrote, "we’re not aware of personally identifiable customer data being
impacted and the code also did not have the ability to request customer
credentials to gain iCloud and other service passwords," and that the
"malicious code could only have been able to deliver some general
information such as the apps and general system information."
Other
emails indicated that Apple was trying to figure out the importance of
the hack, and how it would tell the victims about it. Matt Fischer,
Apple's vice president for the App Store, wondered whether Apple wanted
to send an email to all of its customers affected by the hack. Fischer
wrote, "Note that this will pose some challenges in terms of language
localizations of the email, since the downloads of these apps took place
in a wide variety of App Store storefronts around the world."
Bagwell responded that alerting all of the potential victims could
be a problem, and that sending an email to each of the victims could
take some time. While Apple said that it would tell every victim of the
hack, that apparently wasn't the case. And back in 2015, Apple said in
an FAQ online (that can no longer be found) that "We’re working closely
with developers to get impacted apps back on the App Store as quickly as
possible for customers to enjoy."
Security firm
Lookout said at the time that, "XcodeGhost’s creators repackaged Xcode
installers with the malicious code and published links to the installer
on many popular forums for iOS/OS X developers." Lookout explained that
"Developers were enticed into downloading this tampered version of Xcode
because it would download much faster in China than the official
version of Xcode from Apple’s Mac App Store."
Some of
the apps that contained the XcodeGhost malware included popular titles
at the time such as WeChat, and the Chinese version of Angry Birds 2.
While the malware did impact a large number of users, the malware itself
was not considered sophisticated or dangerous.
A vulnerability discovered by security firm Check Point Research (via AndroidPolice)
could allow a malicious app to skip the usual security features giving
it access to call and text history. It also gives an attacker the
ability to record conversations.
The Qualcomm
Modem Interface (QMI) software is normally impossible for third-party
apps to access, but if key aspects of Android are hacked, the QMI
vulnerability can be used to listen in and record an active phone call,
and as we already pointed out, steal call and SMS records.
QMI is used on as much as 40% of Android handsets including those
made by Google, Samsung, OnePlus, LG, Xiaomi, and more. Check Point kept
certain information out of its report to make sure that the attack can
not be easily copied. There is no indication that the attack has been
used by a malicious hacker.
Check Point
revealed all of this to Qualcomm last October calling it a high-rated
vulnerability. The chip maker told the phone manufacturers that use
Qualcomm's modem chips. So far, the vulnerability has not been fixed and
we can only hope that Qualcomm and Google will patch this in a future
security update.
However, Qualcomm says that it did made fixes available to "many"
Android phone manufacturers last December and that these firms passed
along security updates to end users. The vulnerability will be part of
the June Android bulletin.
Qualcomm issued a
statement today that said, "Providing technologies that support robust
security and privacy is a priority for Qualcomm. We commend the security
researchers from Check Point for using industry-standard coordinated
disclosure practices. Qualcomm Technologies has already made fixes
available to OEMs in December 2020, and we encourage end users to update
their devices as patches become available."