04 April 2022

Elon Musk scammed people $3.75m from a car deposit

... and the authorities are silent on this.


MANY people think that Mr. Musk is brilliant, smart or maybe even eclectic, but in reality he's a scammer making money from other people's money.

In 2017, he thought of a vehicle and called it the Roadster, with world record breaking 'everything' i.e. ¼ mile, acceleration and electric range, all on paper of course.

So he then though of an ingenious money making scam, where to be part of the 'founders' club, you transfer the full purchase price of the vehicle, USD250,000 to him.

Five years later your money is in his pocket and you STILL have no vehicle!

If you invested that money you gave to 'him' into his company's stocks, you'd have $4 million in the bank.

What a rip off merchant Mr Musk is!

See video:


Report claims Apple saved $6.5 billion by removing charger and EarPods from iPhone boxes

Apple's not giving you a charger with your new phone has nothing to do with 'caring' about the planet but rather about their profits.


When TF International analyst Ming-Chi Kuo told clients in June 2020 that the iPhone 12 series would not include a charger or EarPods inside the box, consumers were stunned. Sure, Apple tried to hide behind the goal of being environmentally friendly and pointed out that by reducing the size of the boxes that the iPhone comes in, 70% more devices could fit on a shipping pallet.

Removing the charger and EarPods from the iPhone box allowed 70% more devices to fit on a pallet


More boxes on a pallet would allow Apple to ship more phones to users at one time. As a result, using smaller boxes would allow Apple to reduce yearly carbon emissions by 2 million metric tons, the company said. That is equivalent to taking 500,000 cars off the road.
 

But not everyone believes that Apple made this move, which was copied by most major phone manufacturers including Samsung and Google, to help the environment. While many will agree that Apple is removing the charger from iPhone boxes for a "green" reason, the "green" they are thinking about is the color of money.

The astute observer will note that Apple started this program with the release of its first 5G iPhone series, the iPhone 12. Could Apple have decided to make up for the extra costs of including a 5G modem and other parts by taking the power brick and the EarPods out of the box? 

According to the Daily Mail, by eliminating the charger and the EarPods from the box, Apple has saved a total of £5 billion thus far. That is equivalent to $6.5 billion. But Apple did not reduce the price of its handsets when it removed the accessories from the iPhone box. At the same time, many iPhone buyers who wanted to fast charge their iPhones only had the 5W adapters that came in the box with older models and were forced to spend $19 for a 20W charger and another $19 to replace the EarPods.

Of course, we might be selling Apple short here. After all, some iPhone buyers might have decided to replace the EarPods, which were free out of the box until Apple removed them, with a pair of AirPods which are currently offered at $129 and up.

If a consumer just wanted to replace the EarPods, that could be arranged for an additional $19. So even if an Apple customer just wanted to add a charging brick and the wired EarPods with his new iPhone, that would cost him an additional $38. When you consider the millions of iPhone units Apple sells each year, this certainly runs into plenty of money flowing into Apple's coffers.

Reducing the size of the box and allowing 70% more devices on each pallet should help Apple reduce its shipping costs by 40% which in turn should allow the company to reduce the price of the phone to consumers. Some analysts have computed that Apple is saving the equivalent of $35 on each iPhone it sells. Yet, there has been no cost reduction from the firm.

Since it announced that it was removing the charger and EarPods from the iPhone box, Apple is believed to have shipped 190 million iPhone units. Totaling up the amount of money that Apple has saved from this cost-cutting move and adding the amount of money it saved on shipping comes to the £5 billion (or $6.5 billion) that the Daily Mail computed. In other words, had Apple passed every penny of savings to its customers, the public could be $6.5 billion richer.

But okay, let's say Apple could keep half the amount it saved. That would still have resulted in the public saving $3.25 billion. And we're not even including the amount of money that the public spent on buying a new charger because they didn't have one, or more likely, wanted one that charged at a speed faster than 5W.

And we're not even including the $293.4 million bucks that the Daily Mail says that Apple customers spent on accessories since the company got stingy about what it puts in the box along with the iPhone.

So let's look at it this way. Apple saved money on shipping and by not having to purchase the charging brick and EarPods that used to go in the box. The public not only didn't save any money, but it also had to shell out to replace the accessories they wanted that they no longer received for "free."

This $6.5 billion goes straight to the bottom line increasing Apple's profits and pushing up the price of Apple's stock. In turn, executives like Tim Cook benefit to the tune of millions of dollars while the public pays to replace the missing accessories. Nice work if you can get it.

Source: phonearena.com

03 April 2022

Ukraine's War Crimes 2022

See screen capture of video below.

While the world is distracted by the mainstream media to focus on the Chris Rock & Will Smith act, other irrelevant topics and that Putin is the 'bad guy', will Ukraine be punished for its war crimes?

We've been forwarded a video showing Ukrainian soldiers taunting bound Russian soldiers, where ultimately they are met with a bullet.


This is just one clip of a few going around.

This footage is available to those who wish to find it, including the authorities, where they do not have to be spoon fed the link, as we should be aware that the 5eyes nations intercept and store all internet traffic.

Can the Ukies really do no harm?

So now the question is will they get away with war crimes?

Our bet is, for sure as that's the narrative.

Why hasn't the mainstream media focused on this atrocious war crime?

There is no 'glory' in war as depicted in the propaganda machine called Hollywood, where certain producer's fiction is allegedly a documentary, e.g. Swinder's List etc.

Spam SMS a 'failure of government'

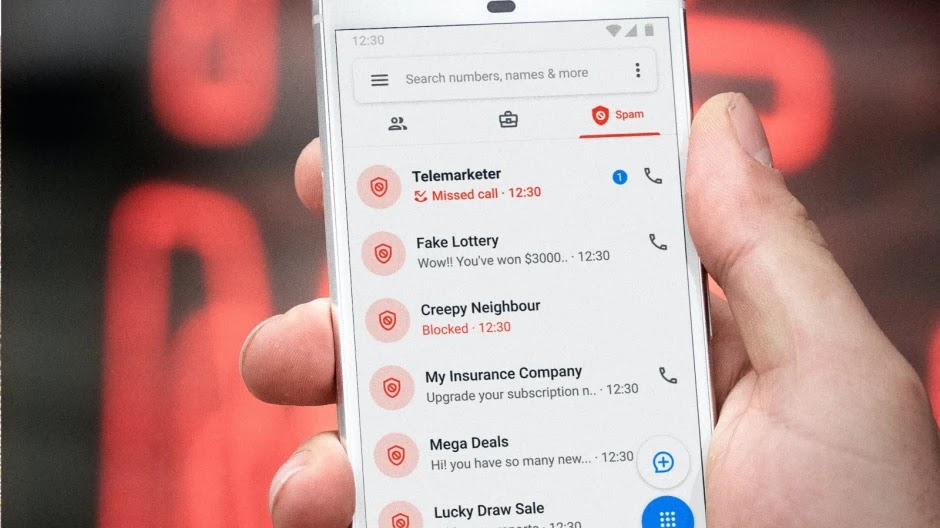
Australians are getting hammered by SMSs sent out by scammers (or rather criminals) in order to defraud the recipient.

Remembering that under 'Commonwealth' law, this is a criminal offence.

Quite simply put, the federal government is letting criminal activity through.

Living under the 5eyes (Tier 1) global surveillance regime is great.

The government keeps ALL the data going in and out of this colony and what you've generated, but if you've lost some info, you just can't ask them for a copy, as it for their use and not yours.

The other great thing (with the 5eyes) is that the governments have implemented other strategies, apparently for your 'protection', like firewalls, so you don't get 'hurt' visiting internet sites.

Here's an example:

Let's just say Hollywoodland put out a great new film, and you want to see it, but you're being geographically discriminated against, by the moguls, where they are not allowing you to see this superb piece of motion picture art.

So, because of this wonderful government invention that has been commercialised, you're able to go to a website, let's make up a name called superflixbybswoodland.com.tv. and view this piece of art.

Instead you may notice the following result:


What this means is that the federal government of Australia has decided that you are not allowed to visit that site by putting it's address into its firewall.

This is done in order not to 'protect' you but rather the business interests of Hollyoodland.

Corporations have control over government actions, period.

With fraudulent SMSs you (the serf) are being exposed to criminal activity where you will actually suffer financially and the government does NOTHING about it.

How easy is it to filter out a message like this?:


Why hasn't this been done a long time ago?

Because the government's really do not care about you (the serf) otherwise it would have been reflected in their actions.

They only care about corporate interests.

You are nothing more than a serf, a slave to corporations.

31 March 2022

Farmer Wants a Wife OH&S breach gagged by NDA

'Reality' shows are a farce!

They are nothing more than producers' wet dream to get 'contestants' (read guinea pigs, lab rats, 'social experiment' participants) to get them to do whatever they want and keep their mouths shut under corporate law called an NDA (Non Disclosure Agreement), which we believe has no lawful legs to stand on, but that's another topic altogether, especially when it comes to breaking the law.

With specific reference to the 2022 production of Farmer Wants A Wife within Victoria we have obtained information from a source that wishes to remain unnamed, for obvious reasons.

While that person may be labelled as a 'whistle blower' that person will NOT be protected under any Whistle Blowing Act of 1984 (by Eric Arthur Blair).

Contestants are told what to say.

They are told what to do and how to act, and if they don't they quite simply won't get paid in the case of FWAW 40% after taping and and the remaining 60% when the show is aired, remembering that they cannot 'squeal' to anyone because they 'voluntarily' signed a (lawful?) contract.

The poor struggling to find a hubby single women MUST purchase their own wardrobe as defined by the producers.

Also, the words that you see in the final product (i.e. on the television) are not the constant's own, but rather carefully scripted ones by the producers.

During taping if they do not get it right, they must repeat them until they do, exactly how the producers want.

So what you see is not the real reactions of the people but rather carefully scripted responses and action/events conjured up by the producers.

Now, here comes the fun part.

The producers abused the women in such a manner that for a lengthy period of time they had to walk an incredible amount of hours in the heat, without water or even a toilet break where as a result one woman fainted.

Once again no one can say anything because if that episode does not air they will not get paid the remaining 60%, and besides they are apparently 'legally' bound by a NDA.

Brilliant way to shut people up, remembering that she 'could' have died as a result of this negligence.

You are being conned by the farce called reality TV and by viewing it you're 'feeding' the scum that deceives you.

30 March 2022

Phone number spoofing

Don’t panic if you get a spam text from your own number


If you have received a spam text message from your own number, you are not alone. As The Verge reported, at the moment, there is a scam campaign going on in which scammers are sending spoof messages to people. You should know that your phone number hasn't been stolen, and you haven't been hacked. Scammers can make it appear as if these messages are coming from customers' own phone numbers, but they are not.

It looks like Verizon customers are the most affected by the spoof message campaign, but customers of other carriers have received such spoof messages as well. The scam text often says that you have paid your bill and offers a free gift.

The message includes a link through which you can supposedly redeem your gift card. It's a good idea not to tap on the link inside. If you tap on it, you risk compromising your phone. Users who have tapped on the link inside the spoof message have been redirected to a Russian website.

What to do in the case of receiving a spoofing message


If you receive a scam message on your phone, it's advisable to forward the spam text to number 7726, no matter which carrier you are using. This will directly send the message to your carrier's spam defense team.

Another thing you can do is file a complaint with the FCC. When you begin filing the complaint in the "Phone Issues" category, choose the "Unwanted Calls/Messages (including do not call and spoofing)" option. Then, choose the sub-issue "my own number is being spoofed," and continue filing the complaint.

Source: phonearena.com

Scott Morrison not sworn in correctly as Prime Minister


According to the PM’s website Scott Morrison was allegedly sworn in to office on the 24th day of August 2018, as the 30th Prime Minister of Australia.

So, what is this ‘oath’ or affirmation, and where is it described?

Australia’s founding legal document, the Constitution is the place where one can find the oath or affirmation.


The transcription of the above is as follows:

I, A.B., do swear that I will be faithful and bear true allegiance to Her Majesty Queen Victoria, Her heirs and successors according to law.

SO HELP ME GOD !

AFFIRMATION.

I, A.B., do solemnly and sincerely affirm and declare that I will be faithful and bear true allegiance to Her Majesty Queen Victoria, Her heirs and successors according to law.

(NOTE.—The name of the King or Queen of the United Kingdom of Great Britain and Ireland for the time being is to be substituted from time to time.)

[ Signature 1] [Edward. H. Alderson]

[Reading Clerk]s

Who was Australia’s first Prime Minister and what was his oath?


After federation, Sir Edmund Barton was the first Prime Minister of the “Commonwealth of Australia”.


The oath that he took, transcribes to the following:

“I Edmund Barton, do swear that I will be faithful and bear true Allegiance to Her Majesty Queen Victoria Her Heirs and Successors according to law?

This is in line with the words from the Constitution.

How is a Prime Minister appointed?

The prime minister of Australia is appointed by the governor-general of Australia under Section 64 of the Australian Constitution,  which means the oath/affirmation must be taken from the last section of the Constitution, that being the Schedule.

What lawfully enacted instrument allows for the change of the oath or affirmation into office?

Since the current so called Prime Minister’s oath does not align with the Constitution, in which lawfully enacted document are the words written with regards to what he stated?

See video:


The words that he said were as follows:

“I Scott John Morrison, do swear that I will well and truly serve the people of Australia, in the office of the Prime Minister and I will be faithful and bear true allegiance to Her Majesty Queen Elizabeth the Second, Queen of Australia, so help me God”.

They are not the words required as per the Constitution, period.

If ‘you’ (the serf) do not state the correct oath/affirmation in court, you cannot proceed with the information you desire to present, your words/testimony/actions cannot be taken into consideration.

It was also revealed that in Tasmania the judiciary’s oath of office was incorrect for 30 years, therefore at law, their orders had no lawful standing, but the effected people did not seek to obtain a remedy from this fraudulent action.

Mr. Scott John Morrison has no lawful standing as Prime Minister of Australia.

The ‘journalists’ have not brought this to the attention of the general population, where even so called ‘constitutional experts’ are silent on this.

What a pathetic farce this colony Australia really is!

P.S. “Queen of Australia”?

What lawfully enacted instrument allows for the creation of such an entity?

28 March 2022

How Thieves Can Hack and Disable Your Home Alarm System

When it comes to the security of the Internet of Things, a lot of the attention has focused on the dangers of the connected toaster, fridge and thermostat. But a more insidious security threat lies with devices that aren’t even on the internet: wireless home alarms. Two researchers say that top-selling home alarm setups can […]


When it comes to the security of the Internet of Things, a lot of the attention has focused on the dangers of the connected toaster, fridge and thermostat. But a more insidious security threat lies with devices that aren't even on the internet: wireless home alarms.

Two researchers say that top-selling home alarm setups can be easily subverted to either suppress the alarms or create multiple false alarms that would render them unreliable. False alarms could be set off using a simple tool from up to 250 yards away, though disabling the alarm would require closer proximity of about 10 feet from the home.

"An attacker can walk up to a front door and suppress the alarm as they open the door, do whatever they want within the home and then exfiltrate, and it’s like they were never there," says Logan Lamb, a security researcher at the Oak Ridge National Lab, who conducted his work independent of the government.

Lamb looked at three top brands of home alarm systems made by ADT, Vivint and a third company that asked that their name not be identified. The Vivint system uses equipment manufactured by 2Gig, which supplies its equipment to more than 4,000 distributors.

Separately, Silvio Cesare, who works for Qualys, also looked, independent of his job, at more than half a dozen popular systems used in Australia, where he lives, including ones made by Swann, an Australian firm that also sells its systems in the U.S.


No matter what the brand or where they're sold, the two researchers found identical problems: All the wireless alarm systems they examined rely on radio frequency signals sent between door and window sensors to a control system that triggers an alarm when any of these entryways are breached. The signals deploy any time a tagged window or door is opened, whether or not the alarm is enabled. But when enabled, the system will trip the alarm and also send a silent alert to the monitoring company, which contacts the occupants and/or the police. But the researchers found that the systems fail to encrypt or authenticate the signals being sent from sensors to control panels, making it easy for someone to intercept the data, decipher the commands, and play them back to control panels at will.

"All of the systems use different hardware but they are effectively the same," Lamb says. "[They're] still using these wireless communications from the mid-90s for the actual security."

The signals can also be jammed to prevent them from tipping an alarm by sending radio noise to prevent the signal from getting through from sensors to the control panel.

"Jamming the intra-home communications suppresses alarms to both the occupants and the monitoring company," Lamb says.

Although some alarms use anti-jamming counter measures to prevent someone from blocking signals from sensors to control panels---if they detect a jamming technique, they issue an audible alarm to the occupant and send an automatic transmission to the monitoring company---but Lamb says there are techniques to beat the countermeasures as well, which he'll discuss at his talk.

One of the Australian products that Cesare examined had an additional vulnerability: Not only was he able to intercept unencrypted signals, he could also discover the stored password on the devices---the password a homeowner would use to arm and disarm the whole setup.


The two researchers plan to present their findings separately next month at the Black Hat security conference in Las Vegas. Lamb will also present his research at theDef Con hacker conference. The researchers both focused on home-alarm systems, rather than commercial-grade models used to secure businesses.

The two researchers each used a software-defined radio to intercept and replay communications. Lamb used a USRP N210, which costs about $1,700. For a serious home-burglary ring, this would be a small investment. Lamb says he was able to do a replay attack---copying signals and sending them back to the system to trigger false alarms---from 250 yards away using this device without a direct line of sight to the sensors. Software-defined radios are controlled with software and can be tweaked to monitor different frequencies. With minimal changes to the code in his SDR, Lamb was able to "have my way in all the systems."

But he could also use an RTL-SDR---a device that costs about $10 from Amazon to monitor signals. These devices don't transmit signals, so an attacker wouldn't be able to disable the alarm system. But he could monitor the signals from up to 65 feet away. Because the transmissions contain a unique identifier for each monitored device and event, an attacker could identify when a window or door in a house was opened by an occupant and possibly use it to identify where victims are in the house---for example, when occupants close a bedroom door for the night, indicating they've gone to bed.

"So as people go about their days in their homes, these packets are being broadcast everywhere," he says. "And since they’re unencrypted, adversaries can just sit around and listen in. Suppose you have a small [monitoring] device to chuck in a [rain] gutter. With minimal effort you could tell when someone leaves the house ... and establish habits. I think there’s some value there and some privacy concerns."


Cesare found that some systems used a remote that let homeowner to arm and disarm their alarms without entering a password on a control panel. This data is transmitted in the clear, also via radio frequency, and can be monitored. He found that most of the systems he examined used only a single code. "I captured the codes that were being sent and replayed them and defeated the security of these systems," he says. Cesare notes that the systems could be made more secure by using rolling codes that change, instead of fixed ones, but the manufacturers chose the easier method to implement with their hardware, at the expense of security.

Cesare was also able to physically capture stored passwords a system made by Swann. All he had to do was attach a microcontroller programmer to read data off the EEPROM. Although he says the firmware was protected, preventing him from reading it, the password was exposed, offering another attack vector to disable the alarm.

Cesare points out that commercial-grade systems are likely more secure than the home systems they examined. "In the home-alarm product, there is an expectation that you're not going to have as strong security as a commercial-grade system," he says. But customers still expect at least basic security. As Lamb and Cesare show, that's debatable.

Source: wired.com

26 March 2022

'Big Data' & governments now have access to your heart.


As we should know 'smart' watches have been around for a while, where they have really been taken up by the mainstream 'consumers' for over a decade now.

Their telemetrics have increased significantly over the years, where now even some sensors are gaining certification as medical tools.

Heart rate is child's play now, where Sp02 (saturation of peripheral oxygen), ECG (electrocardiogram) and 'body battery' terms are becoming the new normal.

While one can obtain whatever information one desires with regards to the functioning/accuracy of smart watches from a plethora of successful reviewers on social media, one of the most important aspects is (deliberately?) left out, that being privacy.

It seems that they're just corporate whores, sponsored by the corporations to spruik their wares, but that would just be a conspiracy theory, right?

While one can read the multinational's 'privacy policy' when installing the companion app to their smart watch, and be besotted by their terminology and (alleged) data privacy policy all this is 'smoke and mirrors'.

Do you know why?

They have your data, you are not in control of it's flow, and your personal information must be given in the companion app before the smartwatch is usable to you, otherwise you will not be able to see 'your' data, the data you create/generate.

Can these corporations program the app without obtaining your exact location or email address or phone number?

Of course they can, but the don't want to, or have a secret agreement with agencies not to, as we now live in a surveillance capitalism world within the 5eyes, 9eyes and 14eyes countries.


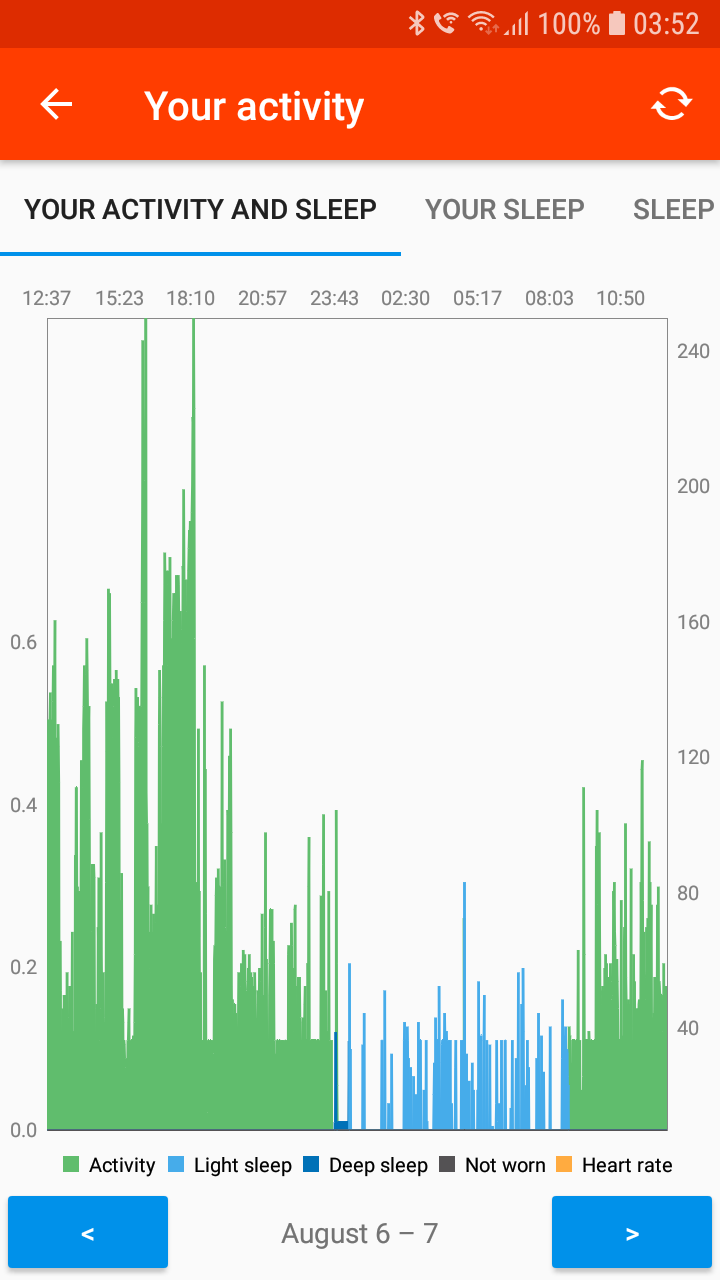
Example of an app that does not require a login or internet to connect to a smart watch.

As always the humble serf (en masse, of course) can change the ways of corporations, but that would require a little bit of work, and we know how lazy the serfs really are, remembering that their silence is acquiescence.

One way to make that change is by quite simply 'voting' with your wallet, i.e not purchasing the product that the corporation 'requires' your data, and stating that to them.

Not all is lost though, as 'hackers' or rather programmers have been looking into the ins and outs of smart watches and have created apps that do not require the use of the internet to use the smartwatch with your phone in order to access that data that you create.

One such app that is open source which can function with a few brands is called Gadgetbridge, which is only available for the Android operating system smartphone.


We do not recommend the use of any Apple devices if your privacy is a concern, irrespective of their marketing jargon.

There are also other smart watch manufacturers that have companion apps that can be used without a login, but that's a hit and miss scenario.