A look into Corporate fraud in Australia, Stranglehold of Monopolies, Telecom's Oppression, Biased Law System, Corporate influence in politics, Industrial Relations disadvantaging workers, Outsourcing Australian Jobs, Offshore Banking, Petrochemical company domination, Invisibly Visible.
It's not what you see, it's what goes on behind the scenes. Australia, the warrantless colony.
Note: Site has more info in desktop mode or 'web version' as seen at bottom of page, when on smartphone.
COMMONWEALTH OF AUSTRALIA (ABN: 122 104 616)
Australia's Prime Minister (CEO) Tony Abbott : "Australia is Open for Business"
They lie to the people every single day, you just have to catch them out!
Evidence shows opposite of Dutton's claims on Cashless Card and family violence rates, advocates say
The Cashless Debit Card was heavily criticised when the coalition
government began trials in 2016, with advocates saying there's data the
policy led to increases in violence.
Advocates have hit back at Opposition leader Peter Dutton's claims
that the abolishment of the cashless debit card would lead to more
family violence in Aboriginal communities.
While visiting Adelaide, Mr Dutton spoke to reporters about the
government’s push to abolish the cashless debit card (CDC), an
initiative for the former coalition government's welfare reform.
The policy quarantined a portion of a person’s welfare income, and it
could not be used to buy alcohol, gambling products, or for withdrawing
cash.
Dutton claimed the removal of the card would see rates of violence
increase in Indigenous communities, in particular, "against women and
children," and prompted the government to focus place its focus on the
issue.
Takes power away'
Change the Record Co-Chair and Djirra CEO, Antionette Braybrook hit
back Mr Dutton’s claims linking the abolition of the card to an increase
in violence.
Instead, saying that the card “takes power away from Aboriginal women”.
“It particularly takes power away from Aboriginal womenwho
need financial control and freedom to make choices that are in their
best interests and the best interests of their children. That is
self-determination,” she said.
The Kuku Yalanji woman has been on the frontline of family violence
prevention for two decades. On Monday, she gave evidence to the CDC
inquiry.
She told NITV News that Mr Dutton was incorrect in his claims.
“Contrary to what Mr Dutton has claimed, there is substantial
evidence that domestic violence police call-outs increased significantly
after the introduction of the Cashless Debit Card - not decreased,” she
said.
“Independent studies across four cashless welfare sites found
an increase in tensions and fighting within households due to the
additional financial pressure that the Cashless Debit Card placed on
families, and increased risk to women fleeing family violence as a
result of having less available money at their disposal.”
Ms Braybrook said the solutions to family violence was not in
government control of money of choices but rather in empowering First
Nations women.
"The solution is to provide culturally safe, trauma-informed,
wrap-around services to support women to find safety and take control
over their own lives and decisions," she said.
"Aboriginal and Torres Strait Islander women are ready to take
control of their own lives no matter where they live, and we just need
to make sure that the appropriate services are there for our woman to do
just that.”
Security researchers have discovered over 80,000 Hikvision cameras
vulnerable to a critical command injection flaw that's easily
exploitable via specially crafted messages sent to the vulnerable web
server.
The flaw is tracked as CVE-2021-36260 and was addressed by Hikvision via a firmware update in September 2021.
However, according to a whitepaper published by CYFIRMA, tens of
thousands of systems used by 2,300 organizations across 100 countries
have still not applied the security update.
There have been two known public exploits for CVE-2021-36260, one published in October 2021 and the second in February 2022, so threat actors of all skill levels can search for and exploit vulnerable cameras.
In December 2021, a Mirai-based botnet called 'Moobot' used the particular exploit to spread aggressively and enlist systems into DDoS (distributed denial of service) swarms.
In January 2022, CISA alerted that CVE-2021-36260 was among the actively exploited bugs
in the then published list, warning organizations that attackers could
"take control" of devices and to patch the flaw immediately.
Vulnerable and exploited
CYFIRMA says Russian-speaking hacking forums often sell network
entrance points relying on exploitable Hikvision cameras that can be
used either for "botnetting" or lateral movement.
Of an analyzed sample of 285,000 internet-facing Hikvision web
servers, the cybersecurity firm found roughly 80,000 still vulnerable to
exploitation.
Most of these are located in China and the United States, while
Vietnam, the UK, Ukraine, Thailand, South Africa, France, the
Netherlands, and Romania all count above 2,000 vulnerable endpoints.
Location of vulnerable Hikvision cameras(CYFIRMA)
While the exploitation of the flaw doesn't follow a specific pattern
right now, since multiple threat actors are involved in this endeavor,
CYFIRMA underlines the cases of the Chinese hacking groups APT41 and
APT10, as well as Russian threat groups specializing in cyberespionage.
An example they give is a cyberespionage campaign named "think
pocket," which has been targeting a popular connectivity product used in
an array of industries across the globe since August 2021.
"From an External Threat Landscape Management (ETLM) analogy,
cybercriminals from countries that may not have a cordial relation with
other nations could use the vulnerable Hikvision camera products to
launch a geopolitically motivated cyber warfare," explains CYFIRMA in the whitepaper.
Weak passwords also a problem
Apart from the command injection vulnerability, there's also the
issue of weak passwords that users set for convenience or that come with
the device by default and aren't reset during the first set up.
Bleeping Computer has spotted multiple offerings of lists, some even
free, containing credentials for Hikvision camera live video feeds on
clearnet hacking forums.
Forum users sharing cracked Hikvision endpoints
If you operate a Hikvision camera, you should make it a priority to install the latest available firmware update, use a strong password, and isolate the IoT network from critical assets using a firewall or VLAN.
The trend of our gadgets and infrastructure constantly, often
invasively, monitoring their users shows little sign of slowing — not
when there's so much money to be made.
Of course it hasn't been all bad for humanity, what with AI's help in
advancing medical, communications and logistics tech in recent years. In
his new book, Machines Behaving Badly: The Morality of AI,
Scientia Professor of Artificial Intelligence at the University of New
South Wales, Dr. Toby Walsh, explores the duality of potential that
artificial intelligence/machine learning systems offer and, in the
excerpt below, how to claw back a bit of your privacy from an industry
built for omniscience.
The Second Law of Thermodynamics states that the total entropy of a
system – the amount of disorder – only ever increases. In other words,
the amount of order only ever decreases. Privacy is similar to entropy.
Privacy is only ever decreasing. Privacy is not something you can take
back. I cannot take back from you the knowledge that I sing Abba songs
badly in the shower. Just as you can’t take back from me the fact that I
found out about how you vote.
There are different forms of privacy. There’s our digital online
privacy, all the information about our lives in cyberspace. You might
think our digital privacy is already lost. We have given too much of it
to companies like Facebook and Google. Then there’s our analogue offline
privacy, all the information about our lives in the physical world. Is
there hope that we’ll keep hold of our analogue privacy?
The problem is that we are connecting ourselves, our homes and our
workplaces to lots of internet-enabled devices: smartwatches, smart
light bulbs, toasters, fridges, weighing scales, running machines,
doorbells and front door locks. And all these devices are
interconnected, carefully recording everything we do. Our location. Our
heartbeat. Our blood pressure. Our weight. The smile or frown on our
face. Our food intake. Our visits to the toilet. Our workouts.
These devices will monitor us 24/7, and companies like Google and
Amazon will collate all this information. Why do you think Google bought
both Nest and Fitbit recently? And why do you think Amazon acquired two
smart home companies, Ring and Blink Home, and built their own
smartwatch? They’re in an arms race to know us better.
The benefits to the companies our obvious. The more they know about
us, the more they can target us with adverts and products. There’s one
of Amazon’s famous ‘flywheels’ in this. Many of the products they will
sell us will collect more data on us. And that data will help target us
to make more purchases.
The benefits to us are also obvious. All this health data can help
make us live healthier. And our longer lives will be easier, as lights
switch on when we enter a room, and thermostats move automatically to
our preferred temperature. The better these companies know us, the
better their recommendations will be. They’ll recommend only movies we
want to watch, songs we want to listen to and products we want to buy.
But there are also many potential pitfalls. What if your health
insurance premiums increase every time you miss a gym class? Or your
fridge orders too much comfort food? Or your employer sacks you because
your smartwatch reveals you took too many toilet breaks?
With our digital selves, we can pretend to be someone that we are
not. We can lie about our preferences. We can connect anonymously with
VPNs and fake email accounts. But it is much harder to lie about your
analogue self. We have little control over how fast our heart beats or
how widely the pupils of our eyes dilate.
We’ve already seen political parties manipulate how we vote based on
our digital footprint. What more could they do if they really understood
how we respond physically to their messages? Imagine a political party
that could access everyone’s heartbeat and blood pressure. Even George
Orwell didn’t go that far.
Worse still, we are giving this analogue data to private companies
that are not very good at sharing their profits with us. When you send
your saliva off to 23AndMe for genetic testing, you are giving them
access to the core of who you are, your DNA. If 23AndMe happens to use
your DNA to develop a cure for a rare genetic disease that you possess,
you will probably have to pay for that cure. The 23AndMe terms and
conditions make this very clear:
You understand that by providing any sample, having your
Genetic Information processed, accessing your Genetic Information, or
providing Self-Reported Information, you acquire no rights in any
research or commercial products that may be developed by 23andMe or its
collaborating partners. You specifically understand that you will not
receive compensation for any research or commercial products that
include or result from your Genetic Information or Self-Reported
Information.
A Private Future
How, then, might we put safeguards in place to preserve our privacy
in an AI-enabled world? I have a couple of simple fixes. Some regulatory
and could be implemented today. Others are technological and are
something for the future, when we have AI that is smarter and more
capable of defending our privacy.
The technology companies all have long terms of service and privacy
policies. If you have lots of spare time, you can read them. Researchers
at Carnegie Mellon University calculated that the average internet user
would have to spend 76 work days each year just to read all the things
that they have agreed to online. But what then? If you don’t like what
you read, what choices do you have?
All you can do today, it seems, is log off and not use their service.
You can’t demand greater privacy than the technology companies are
willing to provide. If you don’t like Gmail reading your emails, you
can’t use Gmail. Worse than that, you’d better not email anyone with a
Gmail account, as Google will read any emails that go through the Gmail
system.
So here’s a simple alternative. All digital services must provide four changeable levels of privacy.
Level 1: They keep no information about you beyond your username, email and password.
Level 2: They keep information on you to provide you with a better service, but they do not share this information with anyone.
Level 3: They keep information on you that they may share with sister companies.
Level 4: They consider the information that they collect on you as public.
And you can change the level of privacy with one click from the
settings page. And any changes are retrospective, so if you select Level
1 privacy, the company must delete all information they currently have
on you, beyond your username, email and password. In addition, there’s a
requirement that all data beyond Level 1 privacy is deleted after three
years unless you opt in explicitly for it to be kept. Think of this as a
digital right to be forgotten.
I grew up in the 1970s and 1980s. My many youthful transgressions
have, thankfully, been lost in the mists of time. They will not haunt me
when I apply for a new job or run for political office. I fear,
however, for young people today, whose every post on social media is
archived and waiting to be printed off by some prospective employer or
political opponent. This is one reason why we need a digital right to be
forgotten.
More friction may help. Ironically, the internet was invented to
remove frictions – in particular, to make it easier to share data and
communicate more quickly and effortlessly. I’m starting to think,
however, that this lack of friction is the cause of many problems. Our
physical highways have speed and other restrictions. Perhaps the
internet highway needs a few more limitations too?
One such problem is described in a famous cartoon: ‘On the internet,
no one knows you’re a dog.’ If we introduced instead a friction by
insisting on identity checks, then certain issues around anonymity and
trust might go away. Similarly, resharing restrictions on social media
might help prevent the distribution of fake news. And profanity filters
might help prevent posting content that inflames.
On the other side, other parts of the internet might benefit from
fewer frictions. Why is it that Facebook can get away with behaving
badly with our data? One of the problems here is there’s no real
alternative. If you’ve had enough of Facebook’s bad behaviour and log
off – as I did some years back – then it is you who will suffer most.
You can’t take all your data, your social network, your posts, your
photos to some rival social media service. There is no real competition.
Facebook is a walled garden, holding onto your data and setting the
rules. We need to open that data up and thereby permit true competition.
For far too long the tech industry has been given too many freedoms.
Monopolies are starting to form. Bad behaviours are becoming the norm.
Many internet businesses are poorly aligned with the public good.
Any new digital regulation is probably best implemented at the level
of nation-states or close-knit trading blocks. In the current climate of
nationalism, bodies such as the United Nations and the World Trade
Organization are unlikely to reach useful consensus. The common values
shared by members of such large transnational bodies are too weak to
offer much protection to the consumer.
The European Union has led the way in regulating the tech sector. The
General Data Protection Regulation (GDPR), and the upcoming Digital
Service Act (DSA) and Digital Market Act (DMA) are good examples of
Europe’s leadership in this space. A few nation-states have also started
to pick up their game. The United Kingdom introduced a Google tax in
2015 to try to make tech companies pay a fair share of tax. And shortly
after the terrible shootings in Christchurch, New Zealand, in 2019, the
Australian government introduced legislation to fine companies up to 10
per cent of their annual revenue if they fail to take down abhorrent
violent material quickly enough. Unsurprisingly, fining tech companies a
significant fraction of their global annual revenue appears to get
their attention.
It is easy to dismiss laws in Australia as somewhat irrelevant to
multinational companies like Google. If they’re too irritating, they can
just pull out of the Australian market. Google’s accountants will
hardly notice the blip in their worldwide revenue. But national laws
often set precedents that get applied elsewhere. Australia followed up
with its own Google tax just six months after the United Kingdom.
California introduced its own version of the GDPR, the California
Consumer Privacy Act (CCPA), just a month after the regulation came into
effect in Europe. Such knock-on effects are probably the real reason
that Google has argued so vocally against Australia’s new Media
Bargaining Code. They greatly fear the precedent it will set.
That leaves me with a technological fix. At some point in the future,
all our devices will contain AI agents helping to connect us that can
also protect our privacy. AI will move from the centre to the edge, away
from the cloud and onto our devices. These AI agents will monitor the
data entering and leaving our devices. They will do their best to ensure
that data about us that we don’t want shared isn’t.
We are perhaps at the technological low point today. To do anything
interesting, we need to send data up into the cloud, to tap into the
vast computational resources that can be found there. Siri, for
instance, doesn’t run on your iPhone but on Apple’s vast servers. And
once your data leaves your possession, you might as well consider it
public. But we can look forward to a future where AI is small enough and
smart enough to run on your device itself, and your data never has to
be sent anywhere.
This is the sort of AI-enabled future where technology and regulation
will not simply help preserve our privacy, but even enhance it.
Technical fixes can only take us so far. It is abundantly clear that we
also need more regulation. For far too long the tech industry has been
given too many freedoms. Monopolies are starting to form. Bad behaviours
are becoming the norm. Many internet businesses are poorly aligned with
the public good.
Digital regulation is probably best implemented at the level of
nation-states or close-knit trading blocks. In the current climate of
nationalism, bodies such as the United Nations and the World Trade
Organization are unlikely to reach useful consensus. The common values
shared by members of such large transnational bodies are too weak to
offer much protection to the consumer.
The European Union has led the way in regulating the tech sector. The
General Data Protection Regulation (GDPR), and the upcoming Digital
Service Act (DSA) and Digital Market Act (DMA) are good examples of
Europe’s leadership in this space. A few nation-states have also started
to pick up their game. The United Kingdom introduced a Google tax in
2015 to try to make tech companies pay a fair share of tax. And shortly
after the terrible shootings in Christchurch, New Zealand, in 2019, the
Australian government introduced legislation to fine companies up to 10
per cent of their annual revenue if they fail to take down abhorrent
violent material quickly enough. Unsurprisingly, fining tech companies a
significant fraction of their global annual revenue appears to get
their attention.
It is easy to dismiss laws in Australia as somewhat irrelevant to
multinational companies like Google. If they’re too irritating, they can
just pull out of the Australian market. Google’s accountants will
hardly notice the blip in their worldwide revenue. But national laws
often set precedents that get applied elsewhere. Australia followed up
with its own Google tax just six months after the United Kingdom.
California introduced its own version of the GDPR, the California
Consumer Privacy Act (CCPA), just a month after the regulation came into
effect in Europe. Such knock-on effects are probably the real reason
that Google has argued so vocally against Australia’s new Media
Bargaining Code. They greatly fear the precedent it will set.
Australia’s Aboriginal welfare problem of the 60s enabled widespread
theft from Indigenous artists – including designs for the one dollar
note.
Reserve Bank of Australia.
David Malangi Daymirringu, Mortuary feast of Gurrmirringu, the Great Ancestral Hunter, 1963.
This year (2016) marks the 50th anniversary of Changeover day: when
Australia swapped from pounds to the new decimal currency. But the “C”
in Changeover day might equally stand for Copyright day, for it marks
the first Aboriginal copyright dispute.
In February 1966, Adelaide’s Advertiser newspaper revealed that the
Reserve Bank had not sought permission from the celebrated Arnhem Land
artist David Malangi when it reproduced his work on the new A$1 note.
Alongside the figures and kangaroos inspired by rock-paintings, the
entire left-hand side of the note was copied from Malangi’s bark
painting, Mortuary feast of Gurrmirringu.
While the media had a field day, the bureaucrats quietly tried to
smooth things out. Malangi was found, then disappeared again. Finally,
in a short ceremony in 1967, Malangi met “Nugget” Coombs, the then
Reserve Bank Governor, who presented him with A$1,000, a medallion and a
fishing kit.
Everybody seemed happy – and history records that Malangi henceforth proudly went by the name “Dollar Dave”.
But were Malangi’s cultural rights respected, and even more importantly, his human rights?
Did Malangi even own copyright over his own painting? Recently
uncovered archival evidence raises troubling questions about the real
nature of the settlement Malangi reached with the Reserve Bank.
Making a dollar
Malangi’s painting was acquired by Czech collector Karel Kupka in early 1963.
While passing through Sydney, Kupka passed on a photograph of the
painting to the Reserve Bank’s Secretary, AC McPherson, who gave it to
the bank’s designer, Gordon Andrews.
David Malangi.
Andrews reproduced much of the detail of the photographed painting for the new dollar design, which was not acknowledged.
Between April 1963 and February 1966, the Reserve Bank somehow forgot
Malangi’s identity – seemingly a straightforward breach of his
copyright.
However, things were not straightforward. In 1963, like most of the Northern Territory’s Aboriginal population, David Malangi was a ward.
The Commonwealth’s Director of Welfare, Harry Giese, was the guardian
of his estate, and the trustee of his property. Malangi couldn’t buy or
sell goods worth more than ten pounds without the Director or a welfare
officer’s consent.
No person could purchase a painting or drawing from a ward except
through an “approved institution”, or with the Director’s consent.
And under section 25 Welfare Ordinance, copyright in Malangi’s work was owned by the Director as trustee for the ward.
In order to buy Malangi’s painting, Kupka needed the “understanding
co-operation” of the Welfare Branch, as well as the Methodist Mission at
Milingimbi.
When Kupka returned to Darwin with his “first great collection from
Arnhem Land” in 1963, he brought his pieces to the Methodist Overseas
Mission storeroom in Darwin’s Knuckey Street. He then displayed them to
the representatives of the Welfare Branch, to show them what he was
taking away.
Why this bureaucracy? The official answer was that it was designed
to combat rip-offs of Aboriginal art. Through the 1950s and 1960s there
was a lively black market trade in Aboriginal objects or “relics”, bark
paintings, “churinga” of stone and wood, and even human skulls.
Missions ran a lucrative trade in Aboriginal art, with most artists
receiving a tiny portion of the profits. In 1965, a Legislative
Councillor alleged that the trade in “native artefacts” was the “most
lucrative business in the Northern Territory”, being one that was not
affected by drought.
Independent Aboriginal artists like Yirawala had to smuggle their own paintings from their home mission to independent galleries.
According to Sandra Holmes, who ran such a gallery in Darwin, the
authorities at Croker Island sold Yirawala’s paintings to interstate and
international dealers, against the artist’s express wishes, and to his
great distress.
Recognising Malangi
When it became aware of the story about Malangi, the Department of
Territories in Canberra wrote – not to Malangi himself, but to the
Northern Territory Administrator. It stated its willingness to,
pay the ruling price for Malangi’s work plus a fee to establish the right to reproduce them in any form in which we desire.
The Reverend Marcel Spengler, the Superintendent at Milingimbi,
politely asserted Malangi’s rights. In a letter in March 1966, he asked
for a royalty, adding that:
we have not been able to house Malangi and his family in a
substantial cottage, and it might be a very good idea for an aboriginal
from this area to be independent in the matter of housing.
With extreme caution, the Reserve Bank wrote that it would
“acknowledge” Malangi’s contribution, adding that “Malangi’s role is not
comparable with that of any other artist concerned in the design of the
new notes but this would not preclude us from making an appropriate
payment to him”.
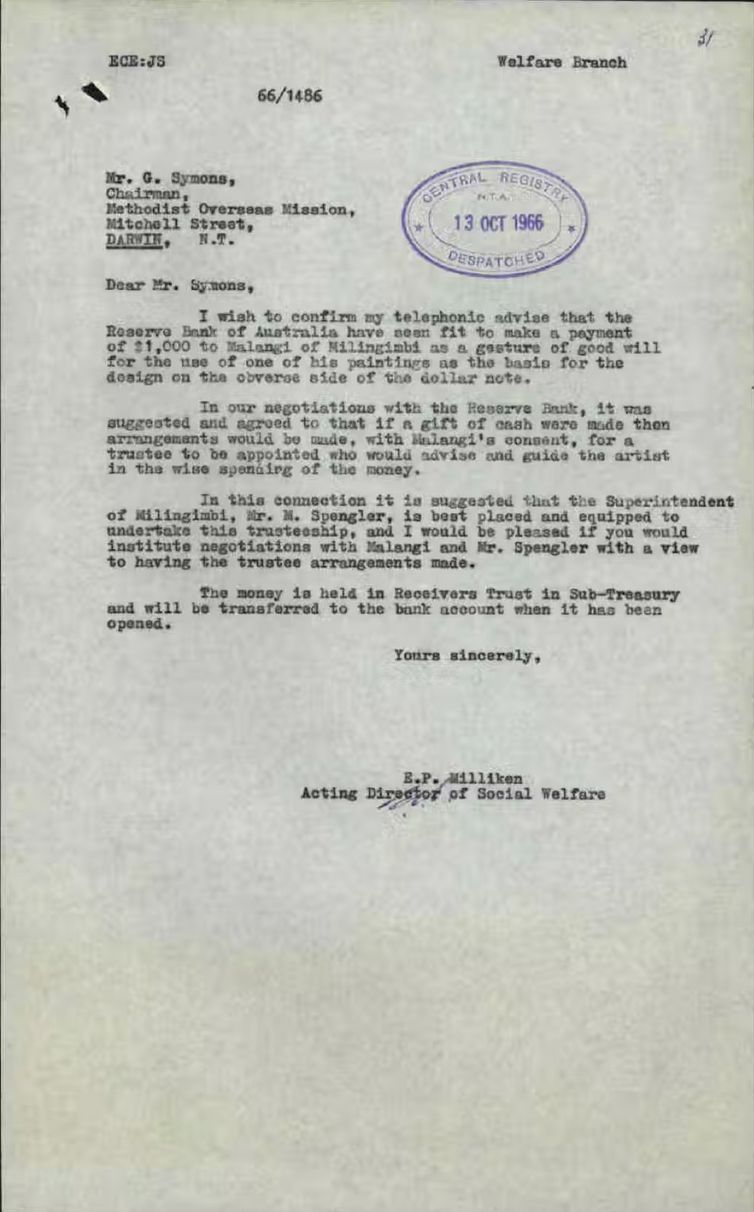
Letter discussing David Milangi’s payment. Australian Archives Canberra, author provided.
By the time the Bank sent a cheque for A$1,000, the Welfare Ordinance had been repealed.
This didn’t prevent the money from going to the Northern Territory
Administrator, who paid it into a trust account “pending a suitable
occasion on which the artist could be presented with a ‘personal
token’”.
The government could no longer legally hold Malangi’s money in a
trust account, or dictate to him how he should spend it. The legal
controls that had existed over his work were undoubtedly
well-intentioned. However, their effect was to facilitate official
rip-offs and prevent artists doing anything about them.
Acknowledging a wrong
There was a post-script. In the Dry Season of 1968, almost a year
after Dr Coombs’ presentation, Malangi indicated his intention to come
to Darwin to make a reciprocal presentation of his own.
Such a presentation would be consistent with Aboriginal law, with the
idea that each party gives the other something to right a wrong.
For example, in 2003 a group of Yolngu men from north-east Arnhem
Land travelled to Darwin to conduct a “wukidi” ceremony at the Northern
Territory Supreme Court.
This was a reconciliation for the famous Tuckiar case,
in which a white police officer, Albert McColl, was speared at Caledon
Bay in 1933. The McColl family travelled to Darwin and met Tuckiar’s
descendants – an example of things being settled the proper way.
Malangi went to Darwin, and stayed at Bagot Aboriginal Community,
under its superintendent’s benevolent gaze. A meeting was arranged with
Dr Coombs for Tuesday 4 June.
There was a reception afterwards. In a note, Giese mentioned that he
had arranged for Malangi to be “available, suitably dressed and on time
with barks to meet Dr Coombs.”
A note on 6 June observed that, “Malangi met Dr Coombs, had barks and was not to his knowledge invited to reception.”
A later unsigned, handwritten note on an official document said:
“Thanks for fixing this […] I did not see Malangi at the reception.”
It’s difficult to know exactly what Malangi was trying to do. If it
was to reciprocate, according to Aboriginal law, then it would seem his
gesture was not properly accepted.
Perhaps, even in 1968, the Aboriginal man did not have suitable clothes.
Google has been sanctioned A$60 million
(around $40 million+) in Australia over Android settings it had applied,
dating back around five years, which were found — in a 2021 court ruling — to have mislead consumers about its location data collection.
Australia’s
Competition & Consumer Commission (ACCC) instigated proceedings
against Google and its Australia subsidiary back in October 2019, going
on to take the tech giant to court for making misleading representations
to consumers about the collection and use of their personal location
data on Android phones, between January 2017 and December 2018.
In April 2021 the
court found Google had breached Australia’s Consumer Law when it
represented to some Android users that the “Location History” setting
was the only Google account setting affecting whether it collected, kept
and used personally identifiable data about their location.
In
actuality, another setting — called ‘Web & App Activity’ — also
enabled Google to grab Android users’ location data and this was turned
on by default, as the ACCC noted in a press release today. Aka, a classic dark pattern. (Actually Google deployed nested dark patterns, plural, as we detail below.)
The regulator estimates that users of around 1.3 million Google
accounts in Australia may have viewed a screen found by the Court to
have breached the Consumer Law.
“This significant penalty imposed
by the Court today sends a strong message to digital platforms and other
businesses, large and small, that they must not mislead consumers about
how their data is being collected and used,” said ACCC chair, Gina
Cass-Gottlieb, in a statement.
“Google,
one of the world’s largest companies, was able to keep the location
data collected through the ‘Web & App Activity’ setting and that
retained data could be used by Google to target ads to some consumers,
even if those consumers had the ‘Location History’ setting turned off.”
“Personal
location data is sensitive and important to some consumers, and some of
the users who saw the representations may have made different choices
about the collection, storage and use of their location data if the
misleading representations had not been made by Google,” she added.
Per
the ACCC, Google took steps to correct the contravening conduct by 20
December 2018, meaning consumers in the country were no longer shown the
misleading screens.
At the time of the court ruling last year,
Google said it disagreed with the findings and that it was considering
an appeal. But, in the event, it decided to take the lumps.
(These
are not as painful as they might have been if the infringements had
occurred more recently: The ACCC notes that the majority of the
sanctioned conduct occurred prior to September 2018 which is before the
maximum penalty for breaches of the Consumer Law was substantially
increased — from $1.1 million per breach to — since then — the higher of
$10 million, 3x the value of any benefit obtained or, if the value
cannot be determined, 10% of turnover.)
The
Court has also ordered Google to ensure its policies include a
commitment to compliance, and requirements that it train certain staff
about the country’s Consumer Law, as well as to pay a contribution to
the ACCC’s costs.
Google was contacted for comment on the sanction. A company spokesperson sent us this statement:
We
can confirm that we’ve agreed to settle the matter concerning
historical conduct from 2017-2018. We’ve invested heavily in making
location information simple to manage and easy to understand with
industry-first tools like auto-delete controls, while significantly
minimising the amount of data stored. As we’ve demonstrated, we’re
committed to making ongoing updates that give users control and
transparency, while providing the most helpful products possible.
Dark patterns inside dark patterns
The ACCC’s press release
includes some screengrabs showing Google notifications to Android users
that the court found to be misleading — which includes three versions
of Google’s Web & Activity setting screen shown to consumers setting
up a Google account on their device that do not mention the word
“location” at all.
Instead, on one — which appeared between April
30, 2018 and December 19 2018 — Google instructs consumers that the
setting “saves your searches, Chrome browsing history and activity from
sites and apps that use Google services”, before nudging them to retain a
pre-selected option to “save my Web & Activity to my Google
account” (aka, opt into Google’s tracking) by suggesting: “This gives
you better search results, suggestions and personalisation across Google
services.” But nowhere does it explain that the user is agreeing to be
location tracked.
If Android users chose to try to turn off
“Location History” — i.e. via a totally separate setting that did not
actually enable them to prevent Google’s location tracking — they could
also be shown a confusing pop-up querying their decision to “Pause
Location History?”, as Google put it, warning them the decision would
“limit functionality of some Google products over time”.
It’s hard
to know what even the point of this was, since the setting did not
empower consumers to entirely prevent Google snooping on their location,
so probably it was mostly there to spread FUD.
The text in this
notification concludes with a further confusing line — telling the user
to “remember, pausing this setting doesn’t delete any previous activity”
— and pointing them to yet more settings where Google suggests they
could “view and manage this information in your Location History map”.
This was presumably intended to send them down a pointless rabbit hole —
while drawing their attention away from the Web & Activity setting
where Google had hidden another location tracking setting.
Other
versions of the Web & Activity setting which the court found
misleading Android users between early 2017 and late 2018 include one
which contains a full five possible actions a user could take —
a surfeit of choice obviously intended to bamboozle them into leaving
the ‘on’ setting as is, since it’s so drastically unclear what anything
else available on the screen means.
“If you use more than one
account at the same time, some data may get saved in your default
account. Learn more at support.google.com,” runs one prominent piece of
cryptic Google small print — without actually hyperlinking the URL in
question to send the consumer to where they might actually ‘learn more’
(or, well, quickly realize there is nothing much to learn and certainly
no ‘off’ switch there).
This chunk of small print mostly appears intended to shield consumers from reading the actual description
of the Web & Activity setting’s function — a setting which,
remember, is defaulted to ‘on’ — since this very salient information is
buried below it (and above a more eye-catching tick-box). But even here
Google is not clear: Again, it does not use the word ‘location’ at all;
there’s only an indirect reference to “Maps” buried in a list that
foregrounds ‘faster searches’ and ‘customized experiences’ to nudge
consumers to agree.
By using the name of its popular Maps product
as a stand in for location Google appears to be suggesting that Android
users need this setting to be on if they want to use Maps — rather than
making it plain that the setting refers to its ability to track their
location.
The same setting screen also includes a
pre-ticked check-box next to yet more text that states: “Include Chrome
browsing history and activity from websites and apps that use Google
services” — so Google is seemingly unbundling tracking settings,
presumably as a back-up in case one of these pre-checked settings gets
unchecked, meaning it can at least grab data via the other.
After
that there’s more small print, lodged under the bland rubric “data from
this device”, which reads: “Control reporting of App Activity from this
device”. However this text is not instantly visually linked to any
setting the user is able to interact with — so anyone glancing at it
might assume it’s not pointing them to an option at all and skip over
it.
Airgapped below, towards the very bottom of the screen, is a
hyperlinked option to “MANAGE ACTIVITY”. This text is bolder — being in
ALL CAPS. So does draw the eye. Yet what even is this? Why does the user
have to wade into fresh Google submenu hell to try to turn off
tracking, as this option seems to be implying? Surely they can just
toggle the ‘on’ switch at the top of the settings screen to do that…
Of
course everything baked into this dark pattern layer cake is pushing
the consumer far away from any understanding of what’s actually going on
with their data in order that they give up and leave the default
tracking on. Truly a masterclass in deceptive manipulative design.
Screengrab: ACCC
A big reboot?
While
Google’s statement today on the ACCC sanction seeks to imply that all
misleading location tracking stuff is in the past, the company is facing
an ongoing investigation into the same practices in the European Union —
open since February 2020
— where it could be on the hook for a more sizeable fine if it’s found
to have infringed the bloc’s General Data Protection Regulation (as
penalties can scale as high as 4% of global annual turnover).
Consumer watchdogs in the EU actually filed complaints about Google’s deceptive location tracking back in November 2018. So Google will still be able to claim it’s moved on — whatever the outcome.
A
draft decision by Ireland’s DPA, which is leading the investigation, is
expected this year — although a final decision could be pushed into
2023 since it must be reviewed by the bloc’s network of DPAs and
agreement reached on any enforcement.
But there’s more — earlier this summer,
European consumer rights groups filed a new series of complaints
against Google — accusing the advertising giant of deceptive design
around the account creation process that they say steers users into
agreeing to extensive and invasive processing of their data.
The
complaints highlight how many more ‘clicks’ are required by Google to
let users opt out of its tracking vs handling it the keys to their data…
so plus ça change right?
The plodding pace of European
privacy law enforcement suggests Google can expect several years’ grace
before any corrective orders land — leaving consumers exposed in the
meanwhile.
But there’s some harder reform on the horizon: EU lawmakers recently agreed
to include a ban on online platforms designing and deploying
deceptive/manipulative and/or confusing interfaces in a forthcoming
flagship update to the bloc’s digital rulebook.
The Digital Services Act (DSA) is generally intended to dial up responsibility and accountability around digital services by steering governance.
On
dark patterns, much will hinge on the specifics of the DSA text, and
its interpretation, clearly — and there may still be wiggle room for
powerful platforms to find ways to use sharkish practices to rob
consumers of their rights and agency. But a key feature of the law is it
entails an active role for the European Commission in enforcement
(against larger platforms — so called VLOPs).
This includes
empowering the EU’s executive to step in and issue guidance on best
practice in areas like interface design. Combined with a new ability to
bare teeth at repeat offenders — as it gets empowered to hit VLOPs with
beefy fines if they break the DSA’s rules — so some of the EU’s
consumer-focused regulation could, suddenly, get rather harder to
ignore. (The DSA will start applying from next year.)
Penalties
for breaches of the DSA can scale up to 6% of global annual turnover. So
the cost and risk of stealing people’s data are certainly rising.
Whether it’ll be enough to give tracking giants pause for thought — or,
what’s really needed, force meaningful reform of privacy-hostile
business models — remains to be seen.
Microsoft has warned today that Windows devices with the newest
supported processors are susceptible to "data damage" on Windows 11 and
Windows Server 2022.
"Windows devices that support the newest Vector Advanced Encryption
Standard (AES) (VAES) instruction set might be susceptible to data
damage," the company revealed today.
Devices affected by this newly acknowledged known issue use AES-XTS
(AES XEX-based tweaked-codebook mode with ciphertext stealing) or
AES-GCM (AES with Galois/Counter Mode) block cipher modes on new
hardware.
While Microsoft mentions the data loss risks on affected systems, the
company does not elaborate on what customers should expect if they're
hit by this issue.
Issue fixed in May and June Windows updates
Microsoft says the issue was addressed to prevent further data damage
in preview and security releases issued on May 24 and June 14,
respectively.
However, these Windows updates also come with a performance hit since
AES-based operations might be two times (2x) slower after installing
them on affected systems running Windows Server 2022 and Windows 11
(original release).
Scenarios impacted by the performance hit might include BitLocker,
Transport Layer Security (TLS) (specifically load balancers), and disk
throughput (especially for enterprise customers).
"We added new code paths to the Windows 11 (original release) and
Windows Server 2022 versions of SymCrypt to take advantage of VAES
(vectorized AES) instructions," Microsoft said when describing the cause
of the issue.
"SymCrypt is the core cryptographic library in Windows. These
instructions act on Advanced Vector Extensions (AVX) registers for
hardware with the newest supported processors."
Microsoft says these Windows updates will restore initial performance metrics once installed on affected devices.
"If this affects you, we strongly urge you to install the May 24,
2022 preview release or the June 14, 2022 security release, as soon as
possible, to prevent further damage," Microsoft added.
"Performance will be restored after you install the June 23, 2022 preview release or the July 12, 2022 security release."
Comment:
h_b_s
"Data damage" the new
marketing gloss over for "data loss" and "filesystem corruption". Don't
be fooled. It's yet another case where Microsoft's bungled agile
development practices have screwed the pooch. Their testing harnesses
are entirely inadequate to support the massive legacy code bases they
have to support in the time scales they need to release.
Dan Andrews support teams are having a
digital identification chip implanted into their bodies in order to
conduct cashless transactions and celebrating this fact preemptively
that it will be 'mandated' on the Victorian population after his
election win in November 2022.
Information has been obtained from a
source close to Andrews with regards to what he is planning after an
election win.
Cashless transactions are a priority of
the 'Nanny State' agenda authorities around the world are
implementing on the serfs.
'Tap & Go' has been a feature of your
physical (credit/debit) card for a while now, where data is only
exchanged between two devices, where that data's initial journey is
to the financial services institution where it gets distributed to
unknown entities to you.
With the advent of the smart phone
together with apps, the tap & go feature has been embedded in the
phone, but now other parties can have access to data emanating from
your phone.
This is great news for 'advertisers',
who can be quite easily masquerading as government actors or 'NGOs'
(Non Government Organisations) and corporations that support this
nanny state style of commerce.
The smartphone is so large and
cumbersome and is so 'last year' where you can also use a smart watch
for cashless transactions.
Why use a smart watch as it is large
cumbersome and so 'last month' compared to a smart ring.
What the Andrews government will do is
'promote' the use of an implanted RFID chip for those who wish to
participate in the trial.
Remember the CallerID 'trial' in
Victoria that became a standard?
The Australian population has also
participated in another trial, as stated by the health minister Greg
Hunt on the 21st of February 2021, where now the serfs are
urged to get a 'quadrella' of shots, which the judiciary is exempt
from (What??? !!! ???? Don't Judicial Lives Matter too???), but that is digression.
See Hunt's statement:
“The world is engaged in the
largest clinical trial, the largest global vaccination trial ever,
and we will have enormous amounts of data. “
This nanny state agenda will not come
into force akin to the frog in boiling water trick.
Over time, services will be decreased
for those who do not have a cashless transaction method available to
them, limiting their movements and participating in the 'digital
economy' (or rather society) the governments are now starting to promote
heavily.
As you have seen over the past few
years Victoria has a be test bed, a PsyOp as to what governments and
corporations can get away with.
The colony has taken quite some time to enact law that may protect consumers/workers/public servants with regards to the I.T world in particular that of data breaches, which have been going on for a few decades now, and the lack of reporting them.
The law is ultra quick to act with regards to gazetting speed measuring equipment which is heavily relied upon for revenue raising, under the pretext of safety.
On February 22, 2018 the Federal Government’s new Scheme for the
mandatory reporting of cybersecurity breaches that result in the loss
of personal data came into effect. Every private and public company
with annual turnover of $3 million or more, listed or not, is now
required to report a cyber breach to the Office of the Australian
Information Commissioner (OAIC) and notify affected customers as soon
as they become aware of a breach.
The threshold for notification under the new Act is more onerous
than most other global jurisdictions, with the test based on whether
the breach “is likely to result” in serious harm to an affected
individual. Mandatory reporting relieves companies from having to
make judgement calls about materiality – ANY breach that ‘is
likely to result in serious harm’ to an individual will be
reportable. This could occur when there is unauthorised access to,
disclosure or loss of customer information held by an entity. Such
information includes personal details, credit reporting information,
credit eligibility information, and tax file number information.
Companies must report the breach within 72 hours.
On 22 February 2018, the Privacy Act 1988 (Cth) (the Act)
was amended to introduce a mandatory data breach notification regime,
the Notifiable Data Breaches scheme (NDB scheme). Australian Privacy
Principle (APP) entities bound by the Act must now report specified
breaches of privacy.
Such data breaches must be notified to the Office of the Australian
Information Commissioner (OAIC). In addition, individuals that are
likely to suffer serious harm as a result of that breach must also be
notified. Businesses need to act quickly to contain and address such
privacy breaches, and practitioners need to be aware of the requirements
and the time frames for action.
The Privacy Amendment (Notifiable Data Breaches) Act 2017 (Cth)
amended the Act to bring into force the NDB scheme. The legislation
introduces a set of onerous reporting obligations for those already
bound by privacy obligations under the Act. The OAIC is already
reporting a flurry of activity in this area. This article outlines the
provisions of the NDB scheme and provides examples of how it may apply
in practice.
The new data breach notification regime will apply to those already
bound by the Act, including businesses with an annual turnover of $3
million or more. Such entities are called APP entities.






h_b_s